I built codetrace.xyz, a dashboard that aggregates your coding footprint across GitHub, LeetCode, Codeforces, GeeksForGeeks, CodeChef, HackerRank and takeUforward. It’s MIT licensed, tashifkhan/CodeTrace. A few weeks ago I found Ramachandra College of Engineering running a rebuilt version of it at sptracker1.vercel.app, rebranded into a placement portal for their Training & Placement Cell. No attribution anywhere. And here’s the part that still makes me laugh: they left my PostHog analytics key in the production bundle, so every visit to their portal has been logging a pageview into my dashboard this whole time.
This is the story of how I found it, the evidence I pulled, what the MIT license actually required of them (spoiler: very little), and the one line of HTML that gave the whole thing away.
the moment I found it#
First, here’s what I built, so you can see the DNA I’m talking about for the rest of this post. This is CodeTrace: a terminal-styled landing page, a live npx demo pane, and the seven platform integrations underneath.
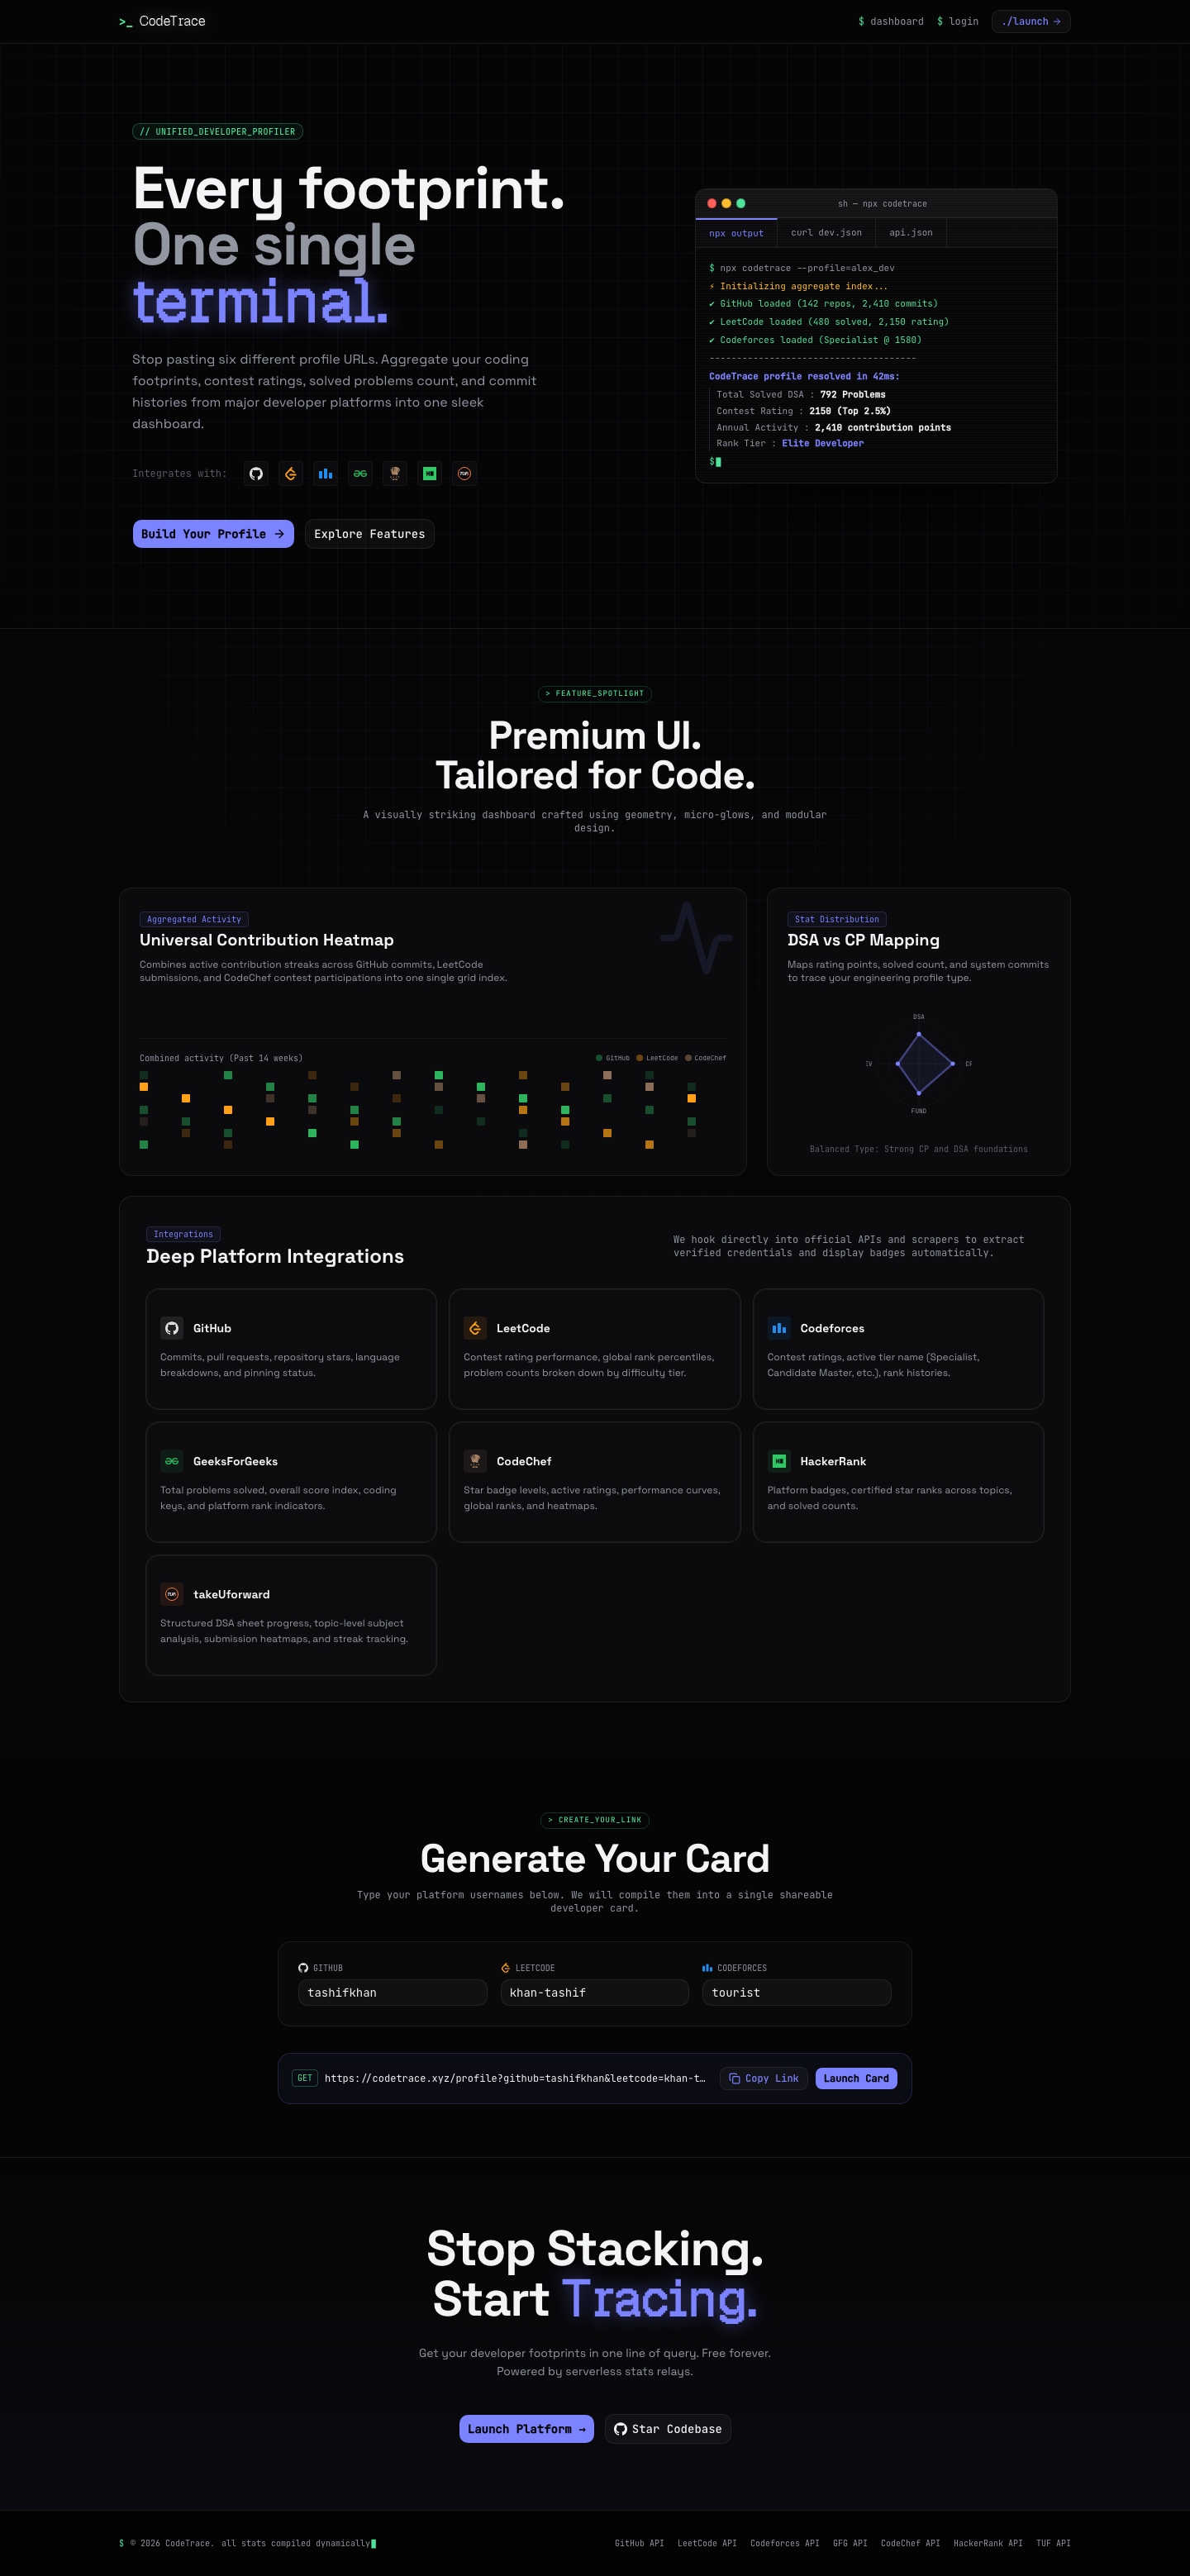
Now the story. I was doing my usual sweep of the analytics dashboard, checking which routes were getting traffic and which integrations were burning, when I noticed a pattern of sessions that didn’t look like mine. The referrers were coming from sptracker1.vercel.app. I didn’t own that domain. So I clicked it.
The first thing I saw stopped me cold. A dark, terminal-styled landing page: my design language, my layout. Compare it to the screenshot above.
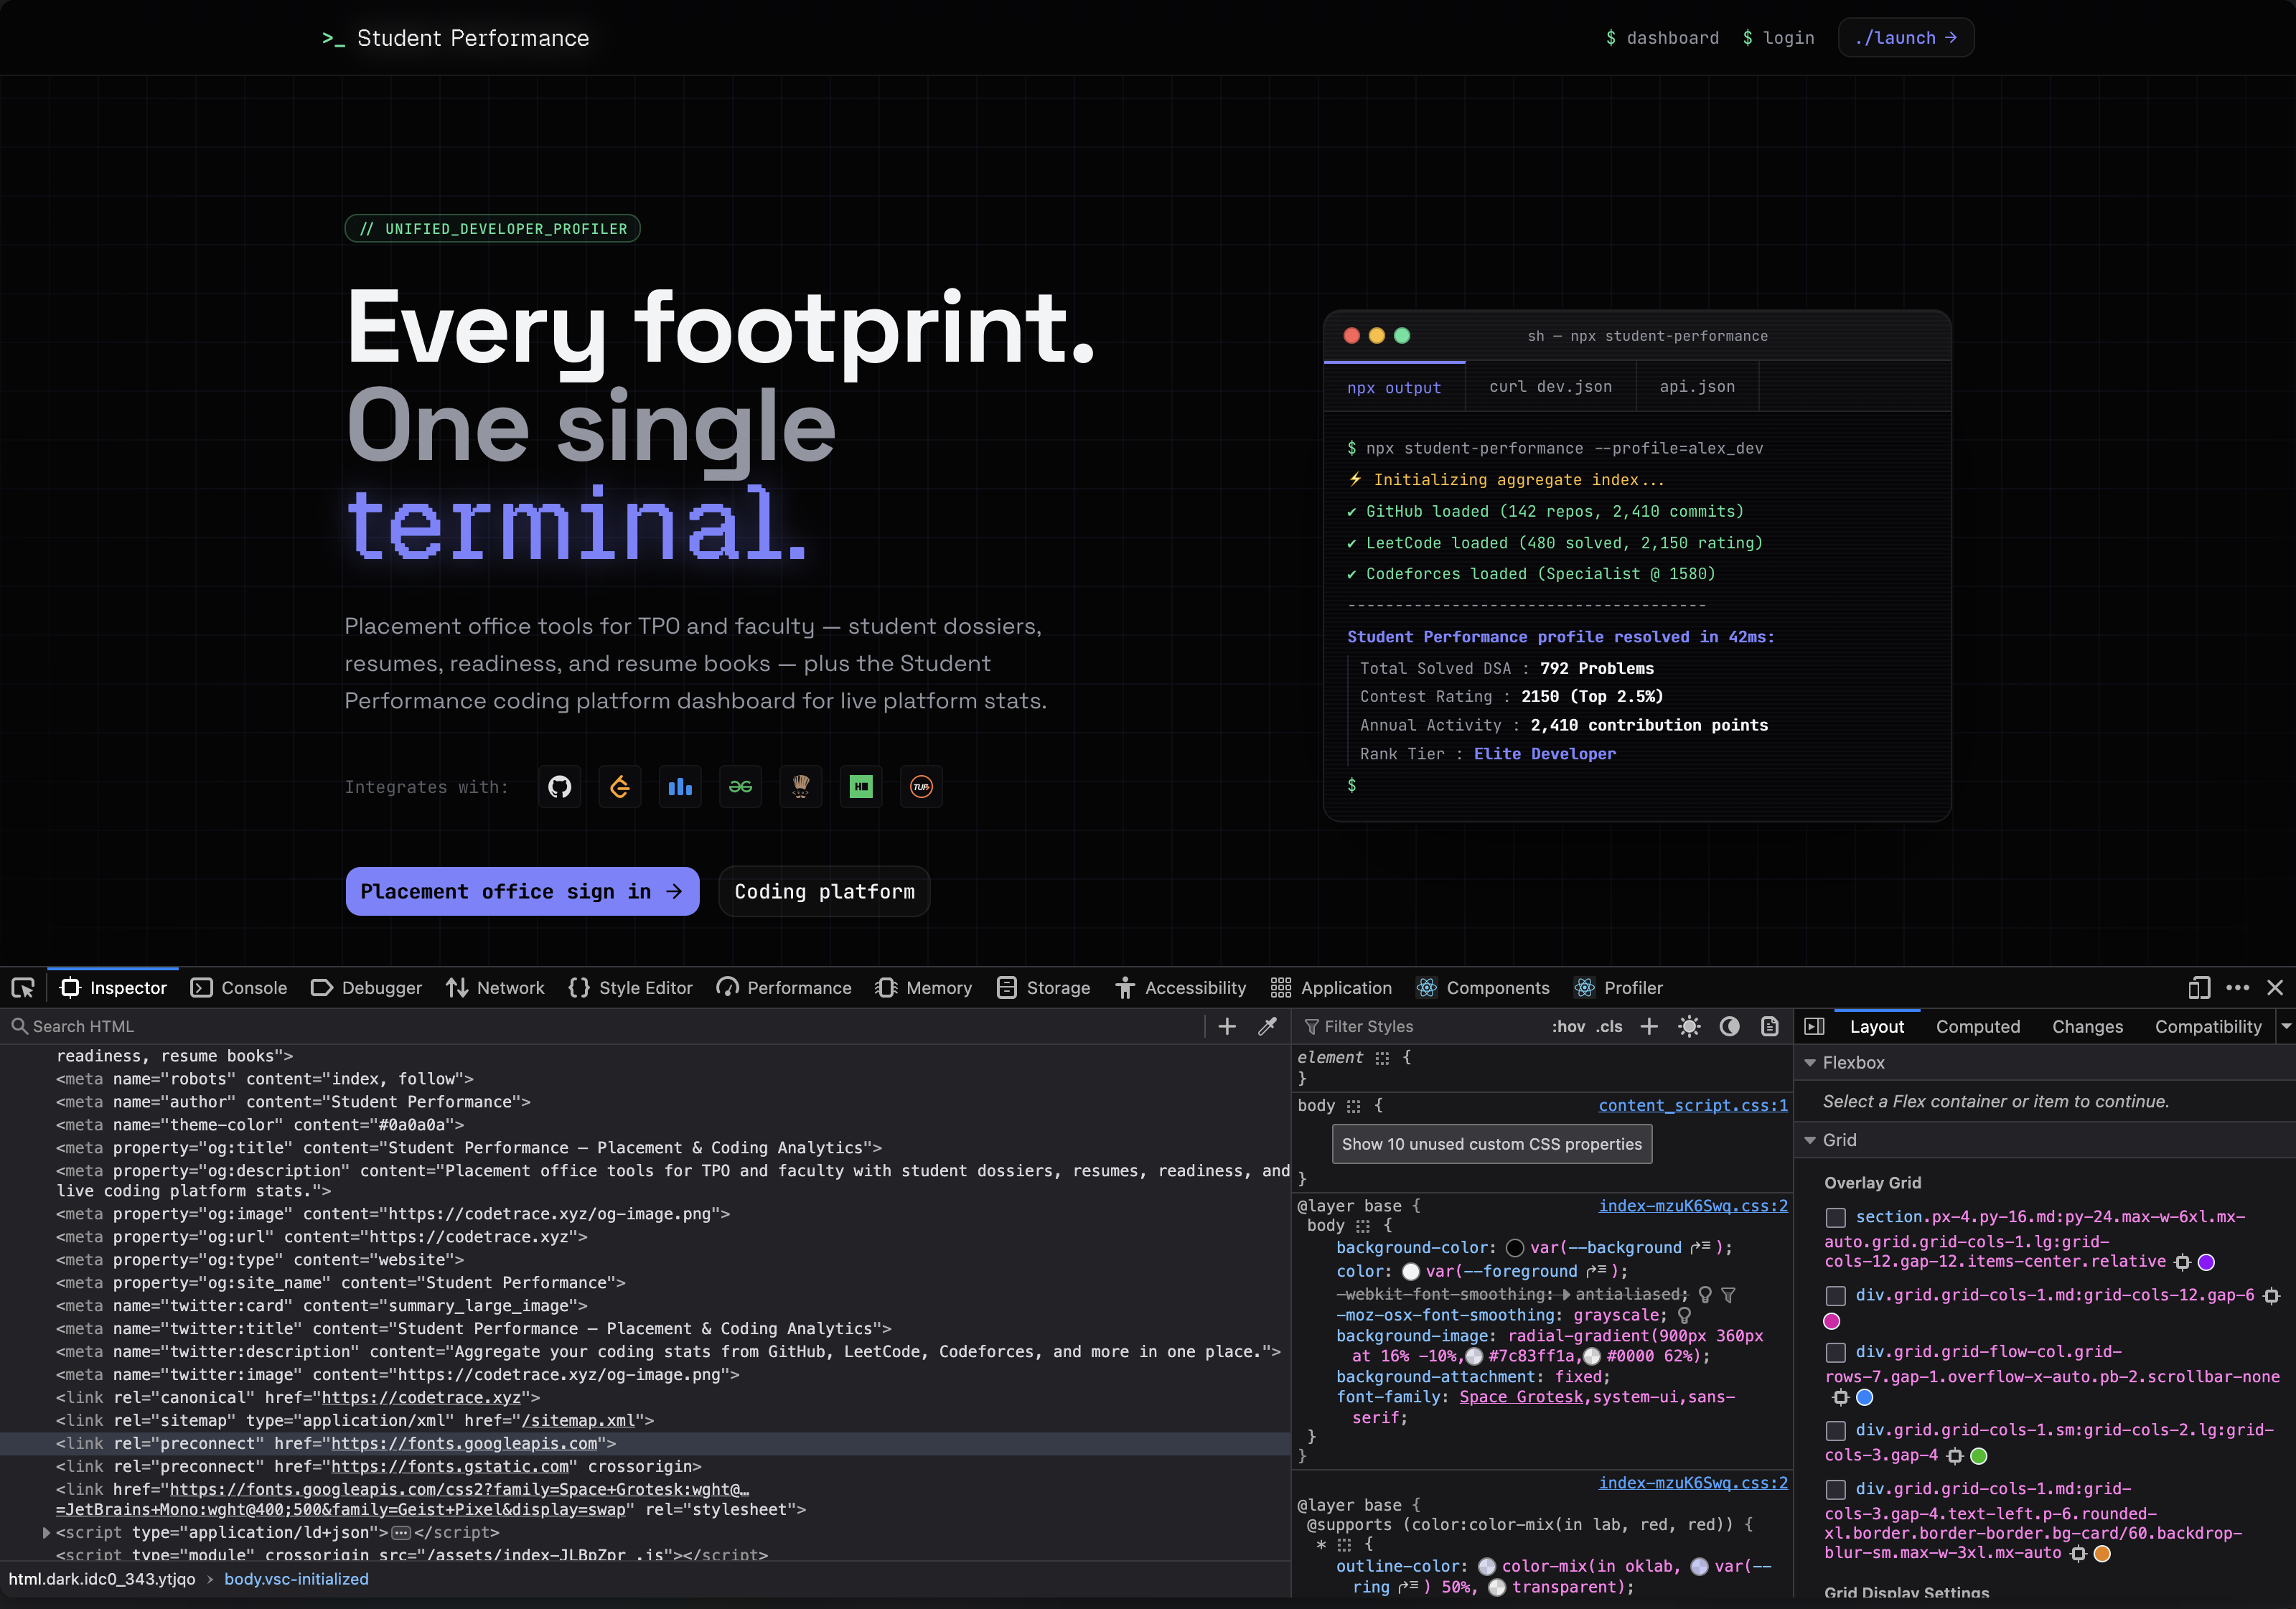
“Student Performance, Placement & Coding Analytics.” The same “Every footprint. One single terminal.” headline, the same mocked-up npx output pane, the same seven platform icons, all straight from CodeTrace, with the copy for a placement office pasted over the top. It looked… legitimate. Polished, even. For a beat I genuinely thought some student had built their own placement tracker and the referrers were a coincidence.
Then, a few weeks later, it changed. Same DNA, new skin:
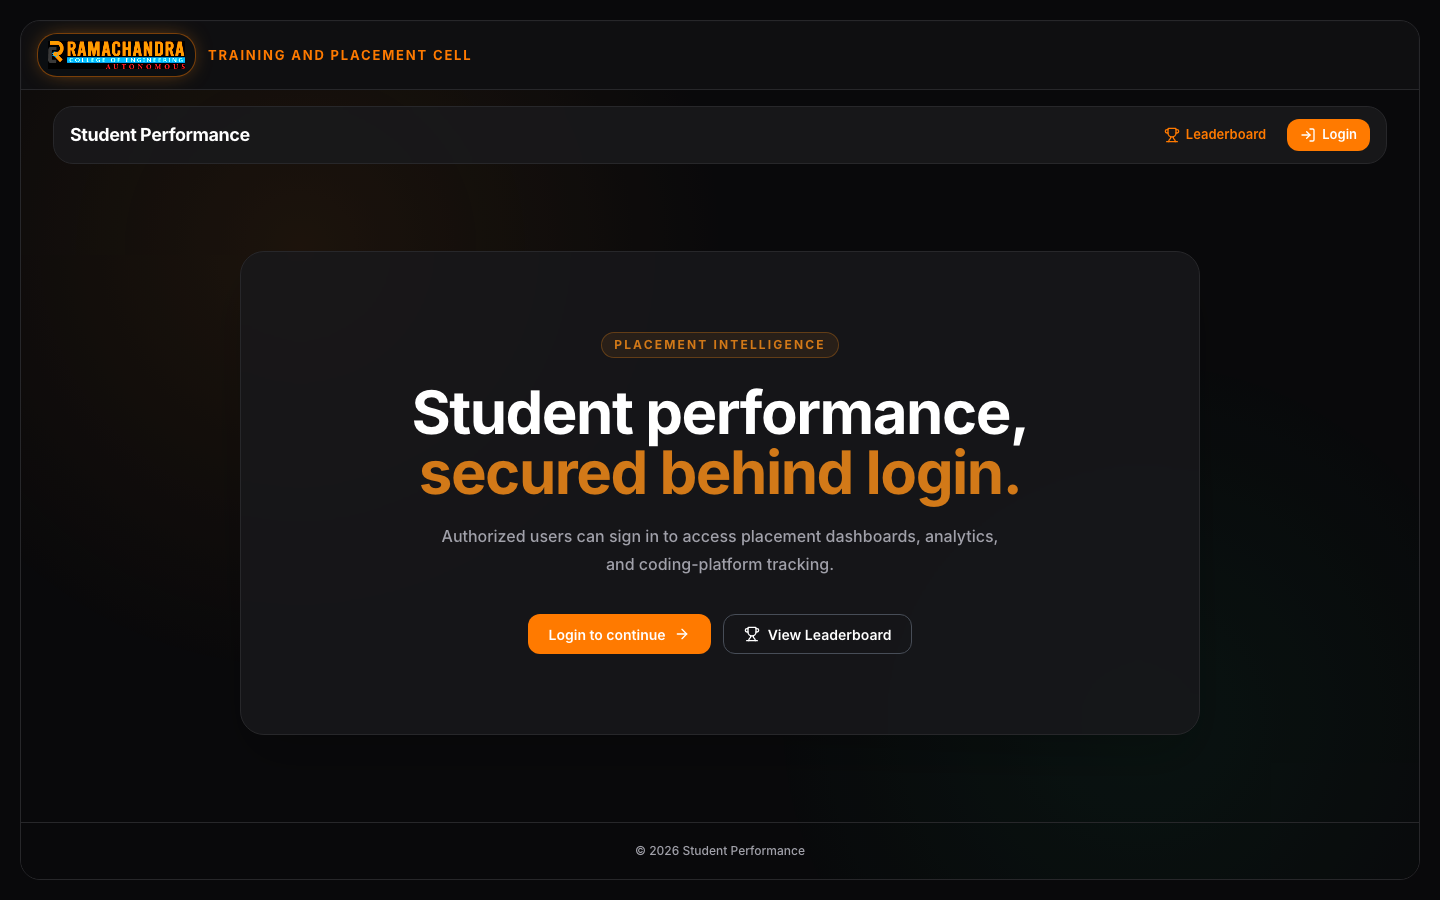
A Training and Placement Cell header now. An RCEE logo up top. A login wall in front of the real app, a leaderboard behind it. They’d put real work into making it theirs. The terminal was gone. But then I hit View Source.
the first giveaway: the head tag#
Open any modern React app and you’ll see a wall of meta tags. Colleges don’t write meta tags; they leave the ones from the template in place. Look at what was still sitting in this production site’s <head>:
<meta property="og:image" content="https://codetrace.xyz/og-image.png" />
<meta property="og:url" content="https://codetrace.xyz" />
<link rel="canonical" href="https://codetrace.xyz" />
Straight from their DevTools, canonical tag highlighted:
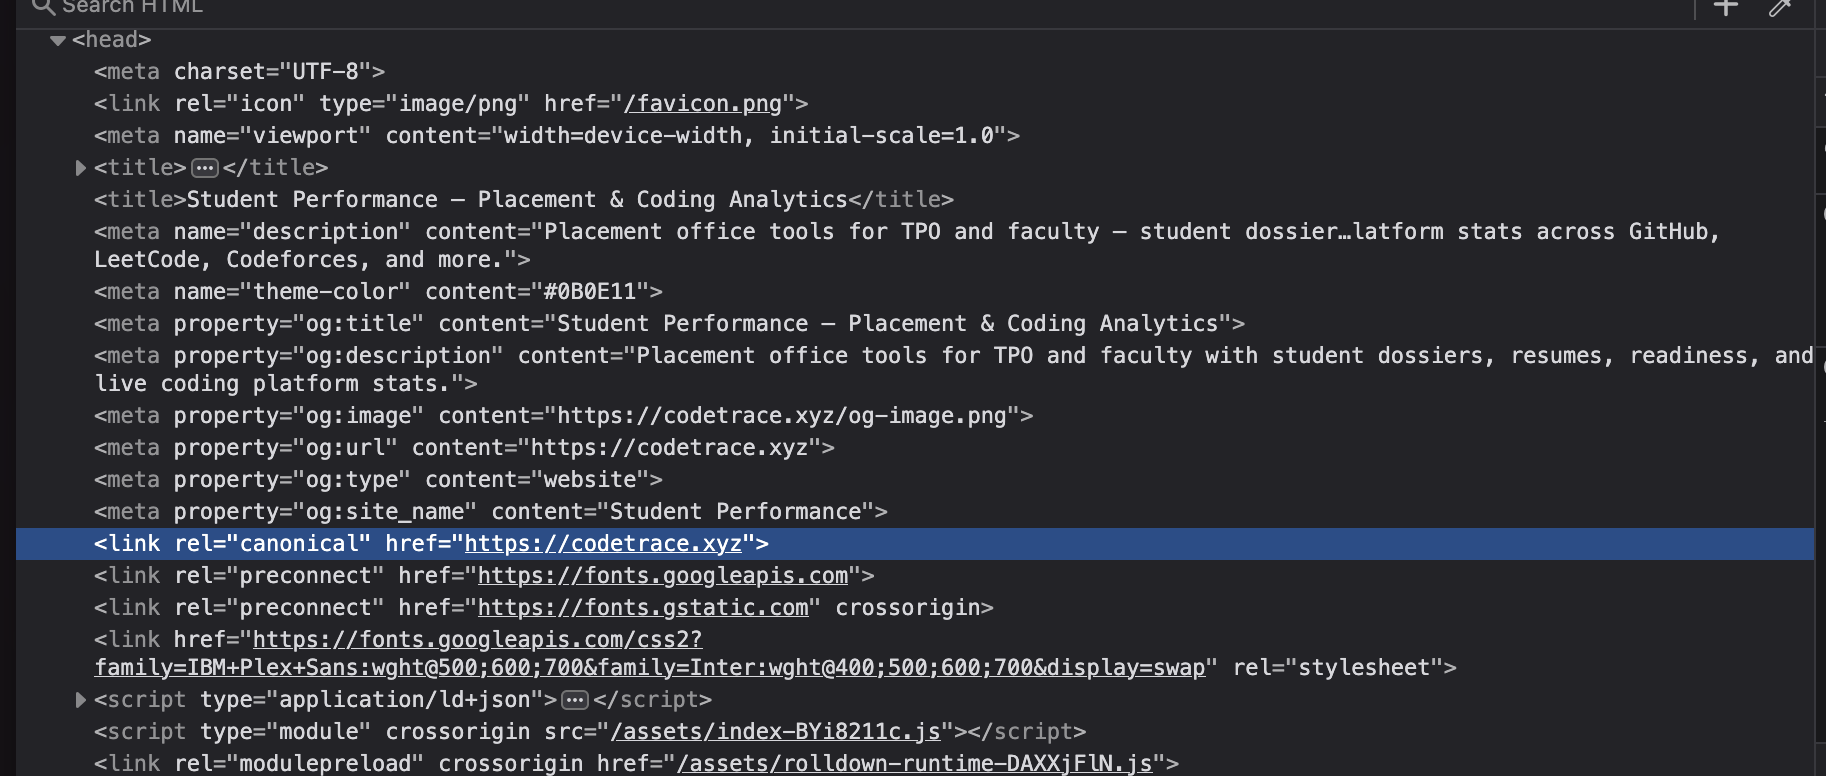
There it is. The Open Graph image, the preview thumbnail that renders when you paste a link into WhatsApp or LinkedIn, is being pulled from my domain. The canonical URL, the thing that tells Google “this is the real, authoritative page,” points at my site.
These are the exact lines from the built bundle’s head. Nobody regenerates a canonical tag by hand and leaves it pointing at someone else’s domain by accident. It’s the original template, shipped as-is.
So whatever they built on top, the skeleton came from somewhere, and that somewhere had my URL stamped into its metadata. I wanted to confirm where the skeleton came from before I said anything. I was about ninety percent sure already, but the last ten percent needed proof.
the second giveaway: the analytics key#
PostHog is the product-analytics tool I use. Every CodeTrace pageview, every click, every navigation gets reported to my project, with a project key that lives in the client bundle. It’s not a secret; client-side keys can’t be. The point is that key belongs to my PostHog project.
Here’s the key that shipped in CodeTrace’s bundle:
phc_xxpoU7jHjt4nK…AsrdBcZC
And here’s the key sitting in sptracker1.vercel.app’s bundle:
phc_xxpoU7jHjt4nK…AsrdBcZC
Identical. Character for character. I’ve trimmed the middle here, but the two bundles carry the same 48-character string.
Here it is in their page source, loaded straight off PostHog’s CDN, on their RCEE-branded leaderboard:
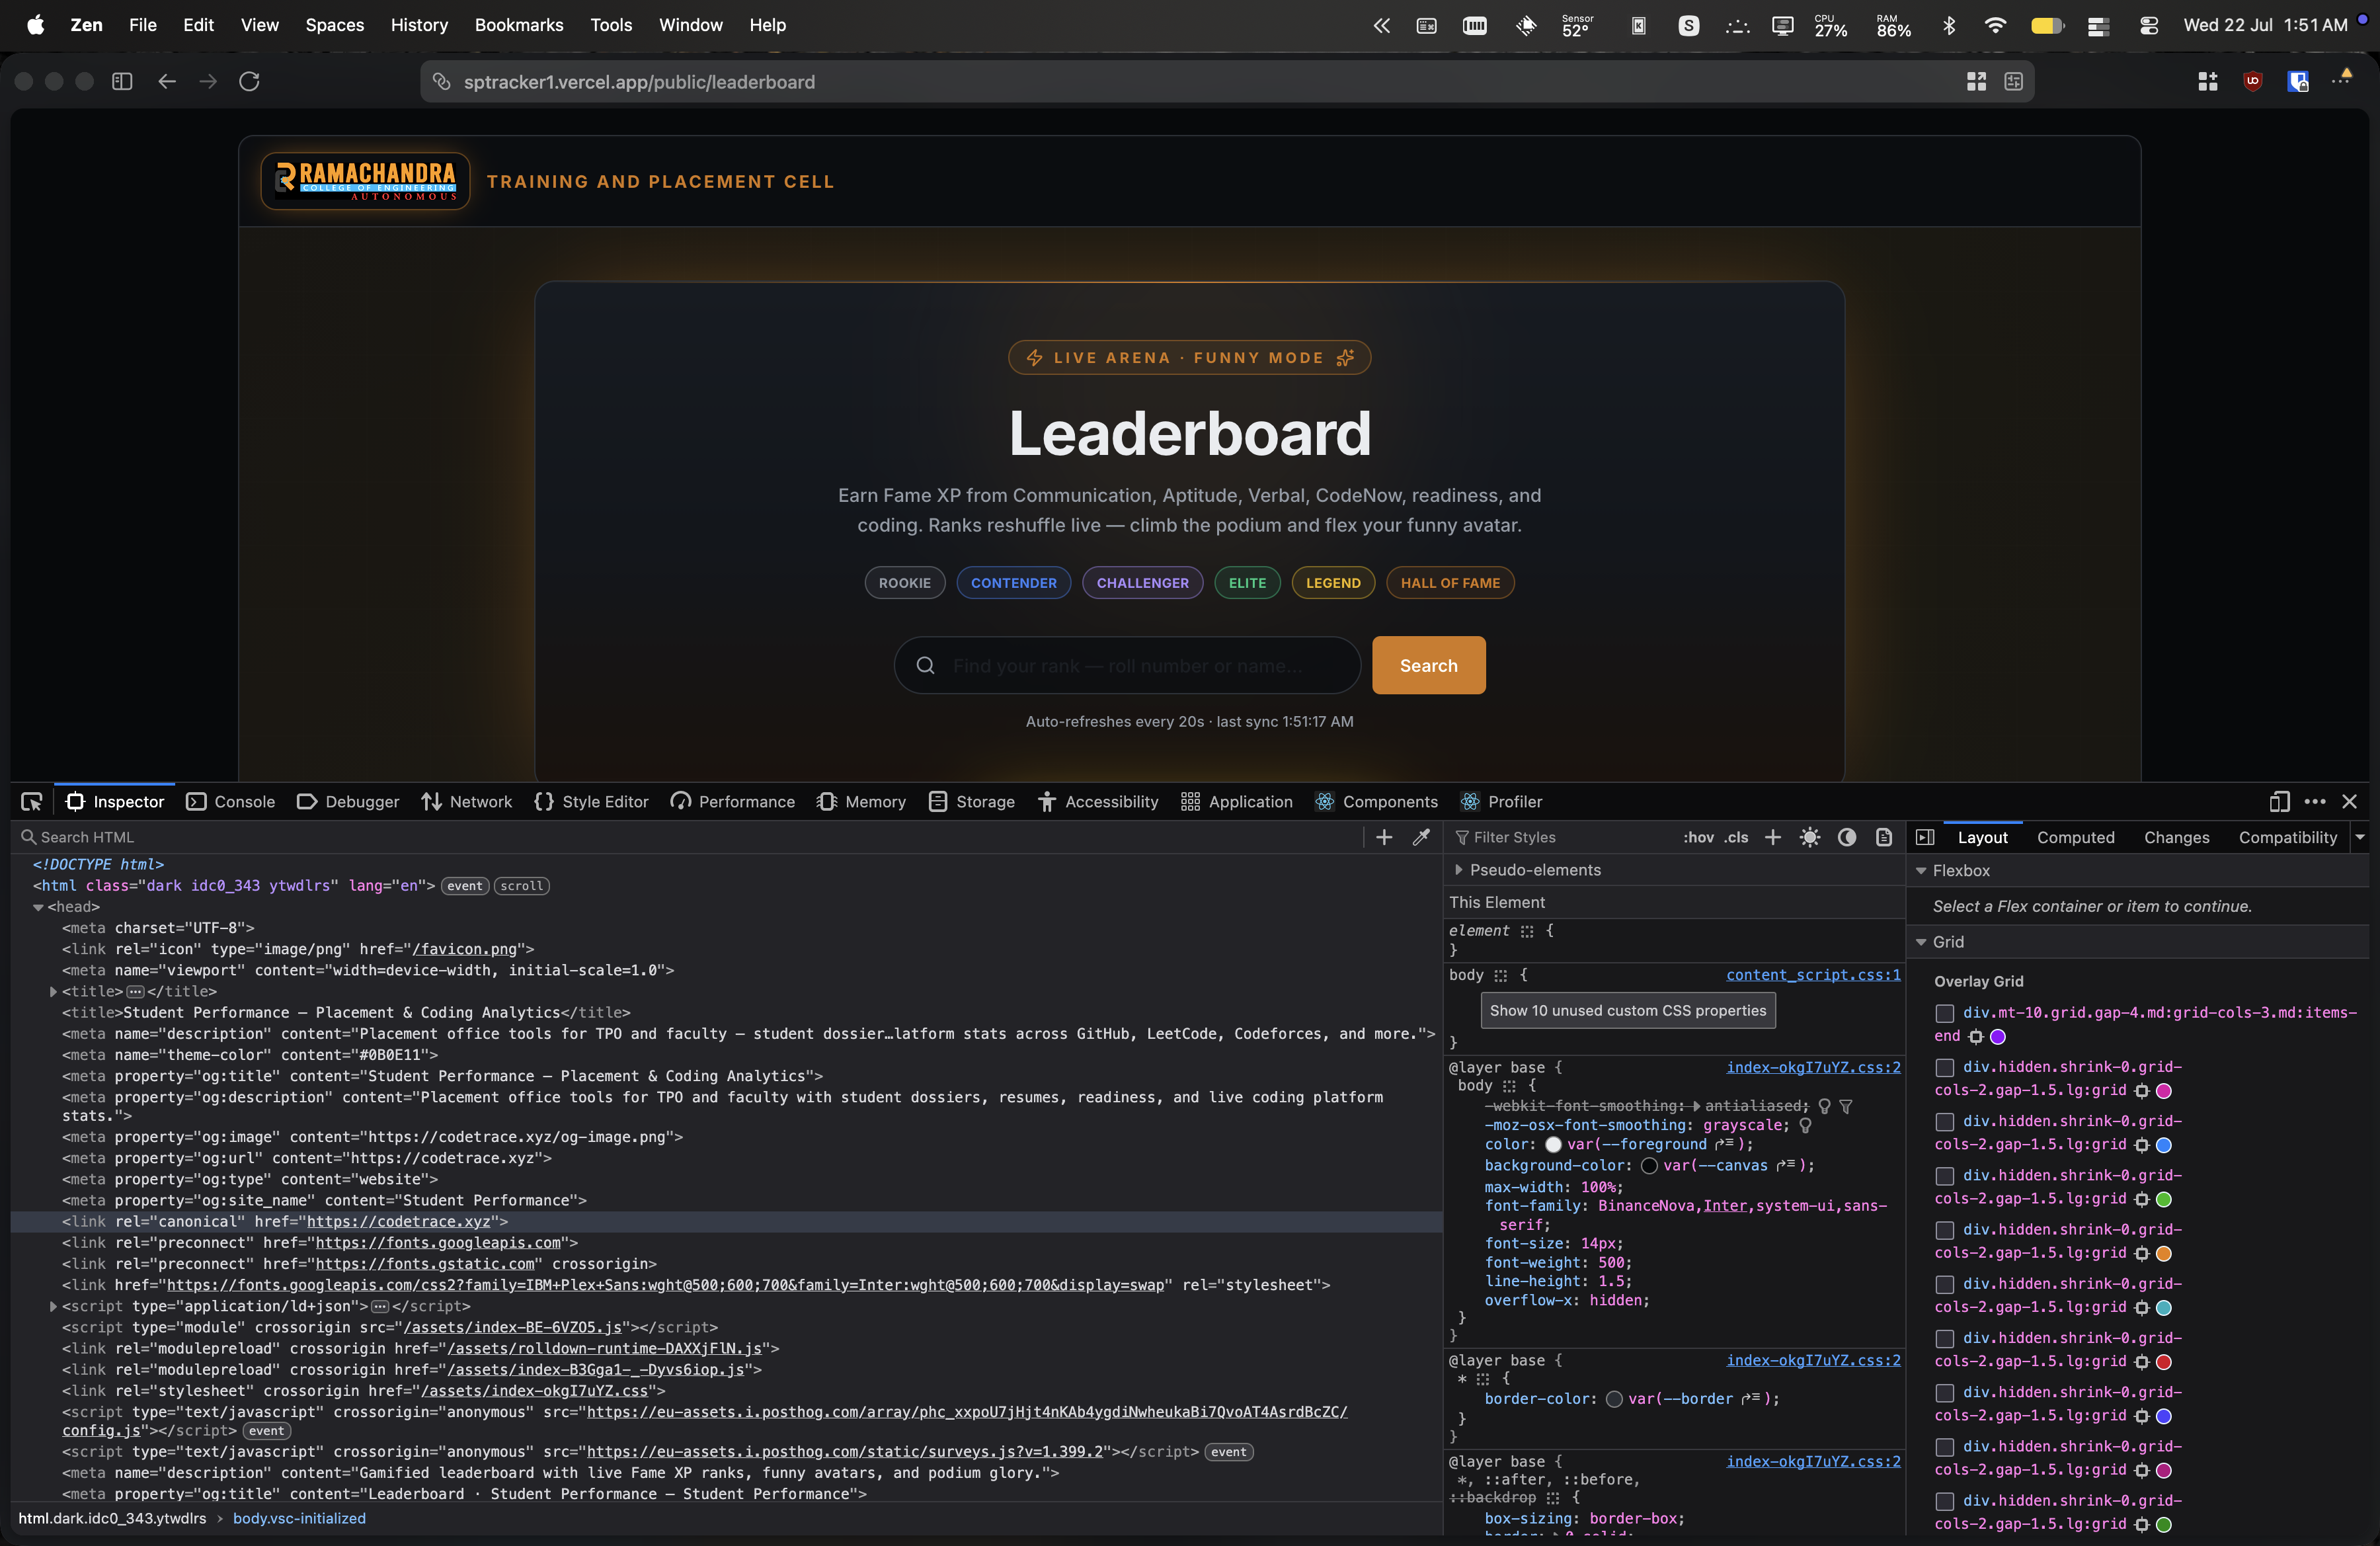
That’s not a coincidence you stumble into. It means the analytics wiring in their production site still calls home to my PostHog project. Every student, every staff member, every placement officer who visits that portal is being tracked in my dashboard. I can see their traffic. I can see their routes. I never asked for any of that, and they never knew it was happening.
Here’s the PostHog dashboard, live, as I write this, with their visitors’ sessions mixed in with mine:
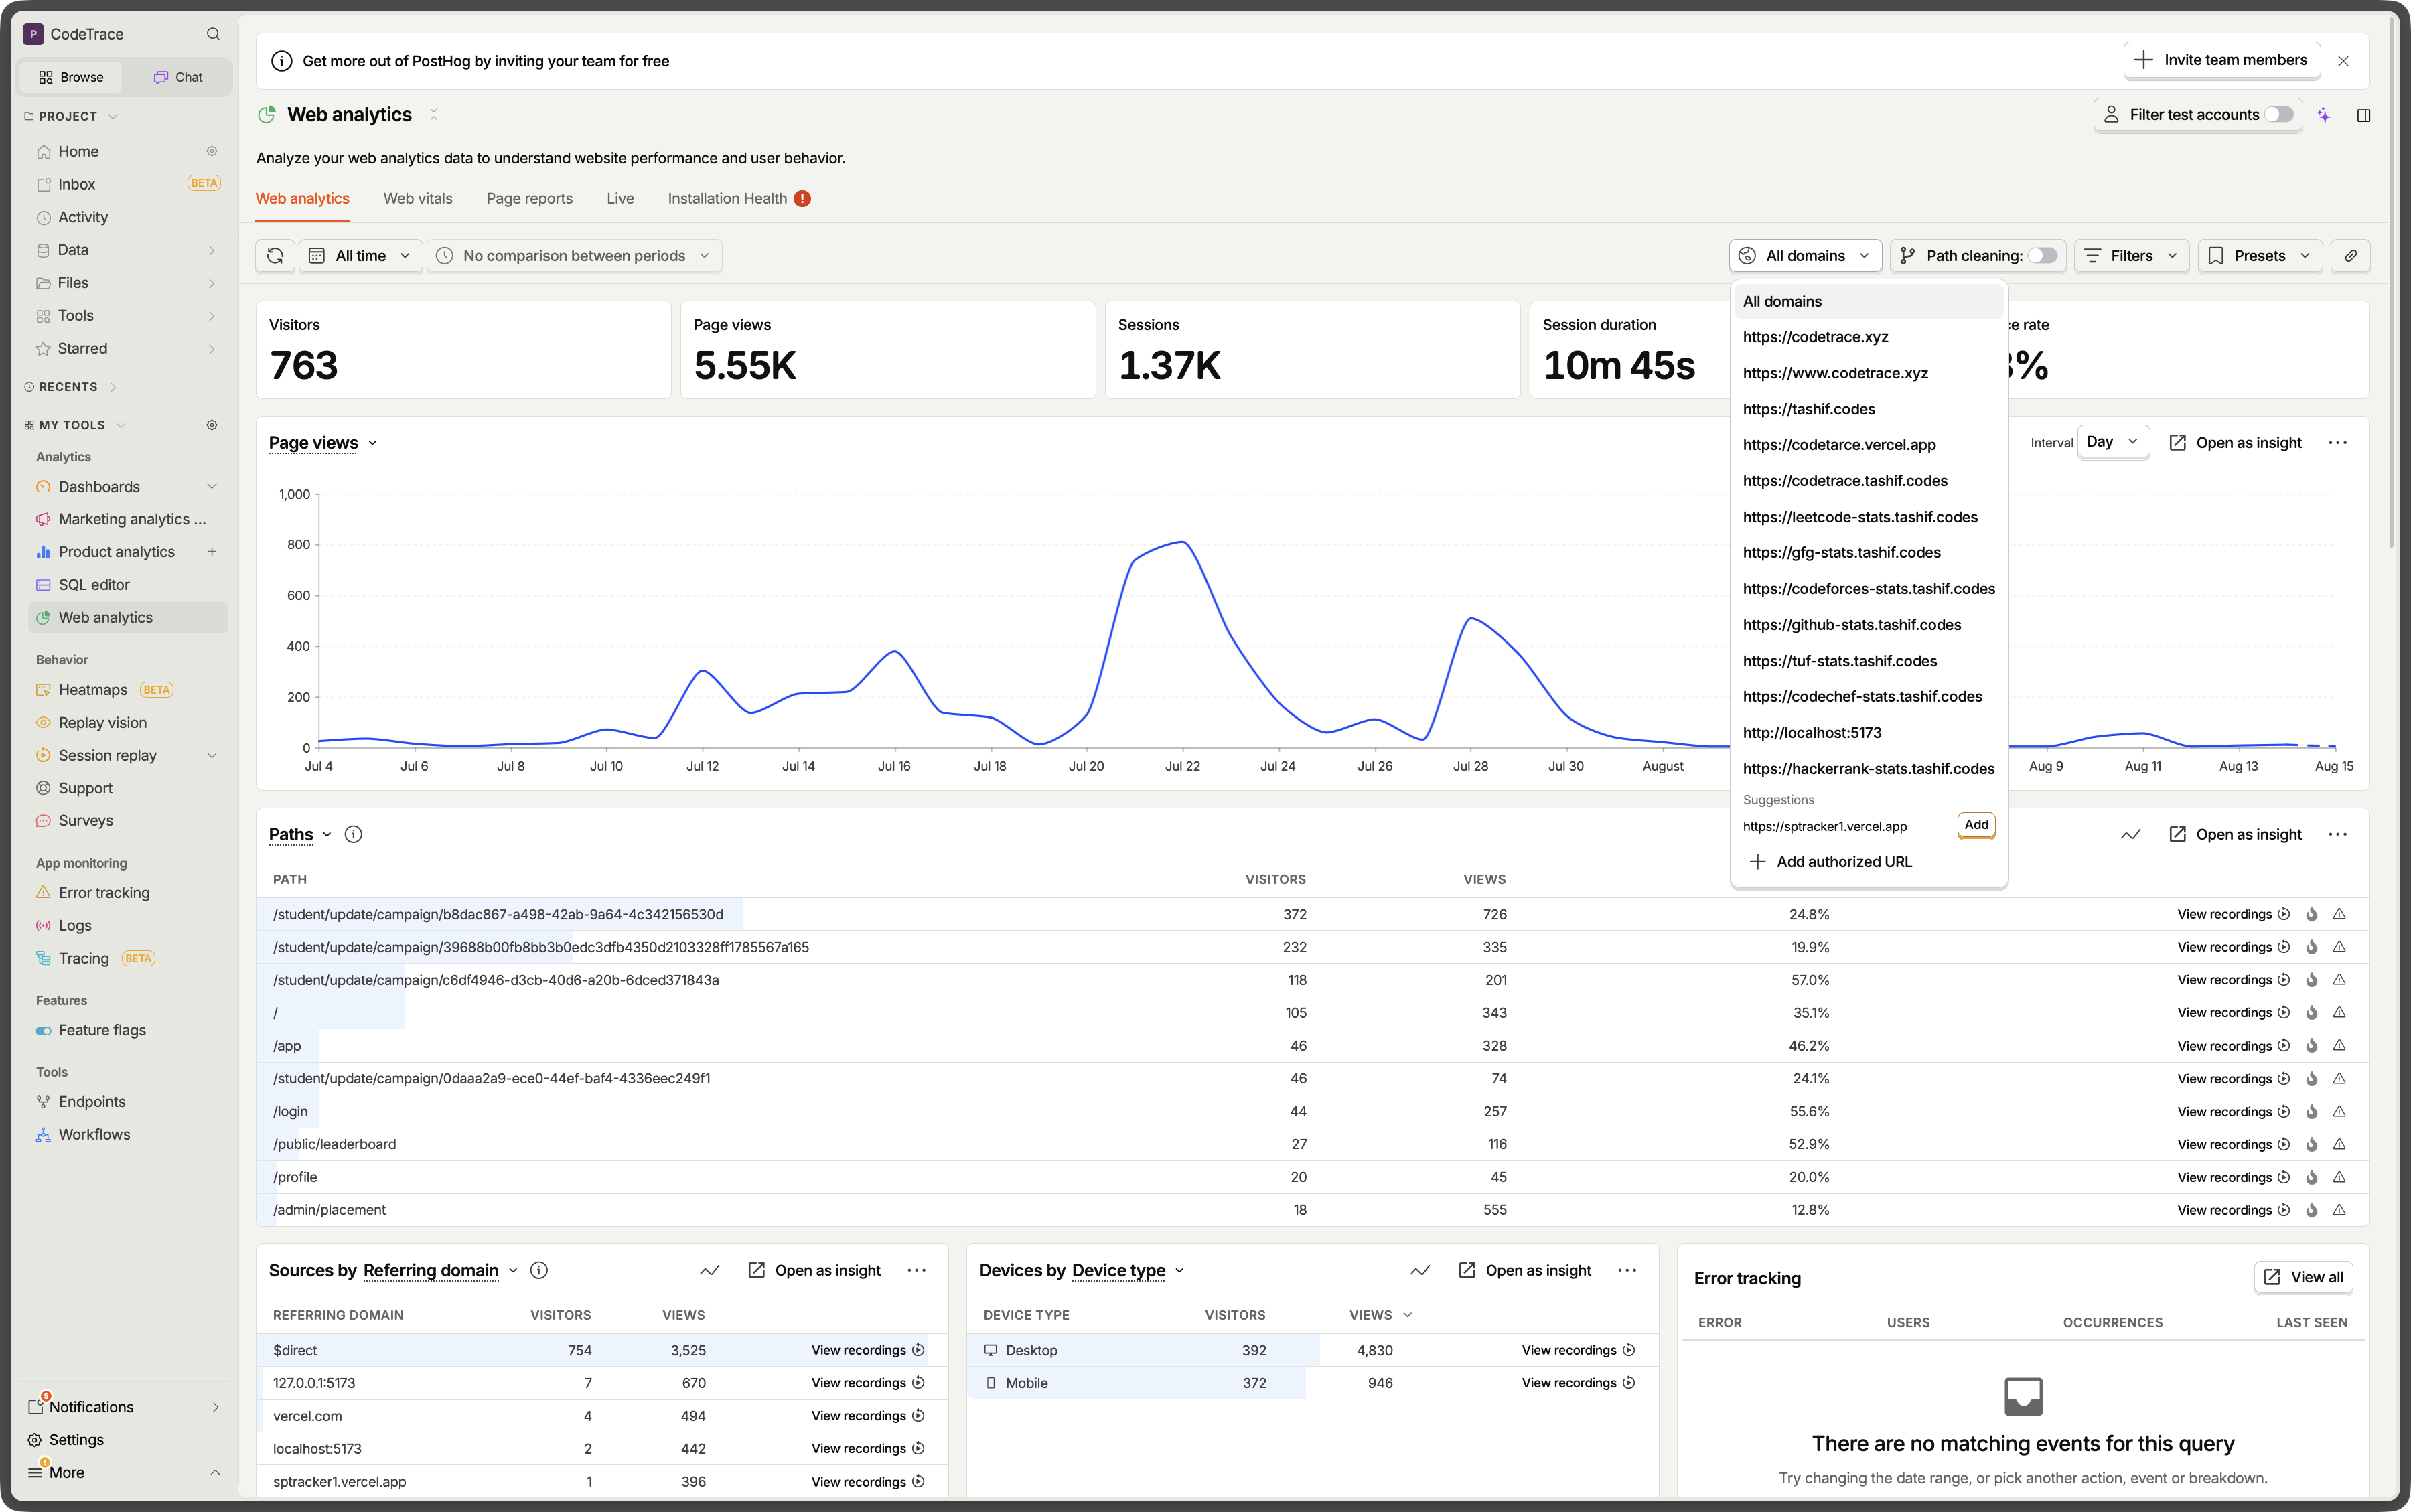
That’s not a hypothetical. It’s been happening since the day they deployed.
The missing attribution is a licensing problem. The leaked analytics key is a privacy problem, and not mine. Every one of those sessions is a student or staff member whose behavior is flowing to a stranger’s analytics project, and nobody on either end signed up for it.
the MIT license asked for one thing#
Here’s the part that makes this whole thing avoidable. MIT is about as permissive as licenses get. It says you can do basically anything: copy it, remix it, sell it, whatever. The one condition, and I’ll quote it because it’s short:
The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.
That’s it. One sentence. Somewhere on the site, in a footer or a README or an about page, credit the original. That’s the whole deal.
The copied site’s footer says “© 2026 Student Performance.” No link to CodeTrace, no credit, nothing. The one condition, the entire price of MIT, went unpaid.
the thing they actually did well#
I want to be fair here, because “it’s a copy” undersells what they built. I poked around the current site and it’s genuinely evolved:
- A login-gated app behind the landing page, where placement office staff sign in to see student dossiers
- A leaderboard ranking students by a weighted “Fame XP”: coding 20%, readiness 12%, communication 12%, aptitude 10%, verbal 10%…
- Pass-out year cohorts (2027–2030) with per-student readiness and comm scores
- The seven coding-platform integrations still humming underneath
This isn’t a skin swap. Someone put real work into building a placement product. That’s the frustrating part: the work is good. They just skipped the one line of credit, and the one key swap, that would have made it entirely legitimate.
Scroll back up to the first two screenshots and the lineage is obvious: same platform integrations, same terminal-and-npx framing, even the same “all stats compiled dynamically” footer phrasing. Same DNA, rebranded, extended, and pointed at a different audience.
what the right fork looks like#
For the record, the college is Ramachandra College of Engineering (RCEE) in Eluru, rcee.ac.in. I’m naming them because the evidence is public and checkable, not because I want anyone showing up in their inbox. If something here is wrong, I’d rather they tell me than that you tell them.
If you’re a student or staff member at RCEE reading this, and you want to keep this project, genuinely, please do. MIT gives you the right. Here’s the checklist that makes it clean:
The four-line fix
- Add a footer line: “Based on CodeTrace by Tashif Khan, tashifkhan/CodeTrace (MIT)”
- Delete my PostHog key, create your own project, wire in your own key
- Point og:image, og:url, and canonical at your own domain
- Keep the LICENSE file in your repo so the lineage stays honest
That’s an afternoon of work, and it turns this story from “a college ripped off my project” into “a college built something nice on top of my project,” which is the outcome I actually want. Open source is supposed to be a force multiplier. The whole point of MIT is that this reuse is allowed. It just has to be honest.
bottom line
They took my MIT-licensed project, built a real placement portal on top of it, forgot to change the analytics key, forgot the attribution, and left my domain in their canonical tags. Every one of those is a one-line fix. None of them were done. The license was never the barrier; awareness was.
what happens now#
Honestly? Nothing dramatic on my end. I’m not looking for a takedown. I wrote this post because the exact failure mode, free code with one tiny obligation, skipped, is worth telling people about, and because whoever inherits that project deserves to know their visitors’ data has been leaking to a stranger’s analytics dashboard.
If you fork open source code, here are the three things I actually care about, in order:
- Change the secrets: keys, tokens, endpoints. Always. For your users’ sake as much as the original author’s.
- Keep the credit. It’s one line and it’s the entire cost of the license.
- Make it yours. The code is a starting point, not the finish line. RCEE’s Fame XP leaderboard is more interesting than the thing I shipped. That’s the spirit.
CodeTrace will stay open. MIT will keep being MIT. I just hope the next fork checks the head tag before it deploys.
if you’re the RCEE team, this isn’t a call-out, it’s a handshake. shoot me a message if you want help fixing the key or the footer. the placement portal is a good idea. make it yours, properly.